01
Threat Hunting & Platform Abuse
Develop hypotheses, correlate diverse telemetry and turn ambiguous signals into high-confidence investigative findings.
Practical guides to home labs, cloud security and the tooling I build for real investigations, drawn from eight years defending large environments.
Field record
Live channel data
Whether you are building your first lab or tightening a production environment, jump directly into the material that moves you forward.
Learn by building
Follow practical walkthroughs for Wazuh, vulnerability scanning, virtual machines and defensive tooling.
Start your first labThink like a defender
Explore security operations, automation and the field-tested thinking behind resilient environments.
Read the field notesUse better tools
See the security software, hardware and creator tools Joshua actually uses and recommends.
Explore the kitI'm Joshua Clarke, a Senior Cyber Security Analyst currently focused on Azure fraud and abuse threat hunting across large-scale cloud environments.
I bring a builder mindset to investigations. Alongside hands-on analysis, I create lightweight tooling and repeatable workflows that help analysts move faster, improve consistency and turn complex findings into practical next steps.
What I bring
Four connected capabilities shaped by hands-on security operations, engineering collaboration and practical education.
Develop hypotheses, correlate diverse telemetry and turn ambiguous signals into high-confidence investigative findings.
Investigate complex security events and improve repeatable forensic workflows across distributed environments.
Build practical tooling that reduces repetitive work, shortens setup time and makes investigations more consistent.
Translate technical findings into clear recommendations, training and practical education for analysts and learners.
Professional record
From enterprise IT and managed detection to consulting, cloud forensics and Azure threat hunting at Microsoft. The through-line is evidence-led investigation, clear communication and tooling that helps analysts move faster.

Microsoft
CurrentJun 2021 - Present · 3 roles
Investigating Azure fraud, abuse and adversarial platform activity across large-scale cloud environments, turning ambiguous signals into findings that support detection, enforcement and disruption.
Selected impact
Led cloud forensic and incident response improvements across globally distributed investigations, combining operational delivery with training, mentorship and analyst tooling.
Selected impact
Led and supported complex investigations across Azure, Microsoft 365, Gaming and corporate environments, including incidents involving advanced threat activity.

Accenture UK
May 2020 - Jun 2021
Established and supported a multi-cloud, threat-led security operations service for a government client, protecting critical national cloud infrastructure.
Analyst who ships
Most analysts work with the tools they're handed. When mine slow me down, I build better ones: triage scripts, automations and platforms that make slow, manual work fast and repeatable. It's the same instinct behind the serverless forensic platform I designed in my day job, which cut analyst setup from hours to minutes.
Almost all of that code lives in private repositories, so my public GitHub looks quiet. GitHub still counts every commit without showing a line of it, so the graph below is the real picture, refreshed every few hours.
99%
of my contributions over the last 12 months went to private repos. 2,508 private, 18 public.
Contribution graph: 2,526 contributions · last 12 months
Proton's Black Friday 2026 sale - the best discounts on Proton VPN, Mail, Pass, Drive and Unlimited, and why these tools belong in every cybersecurity and privacy-focused professional's stack.
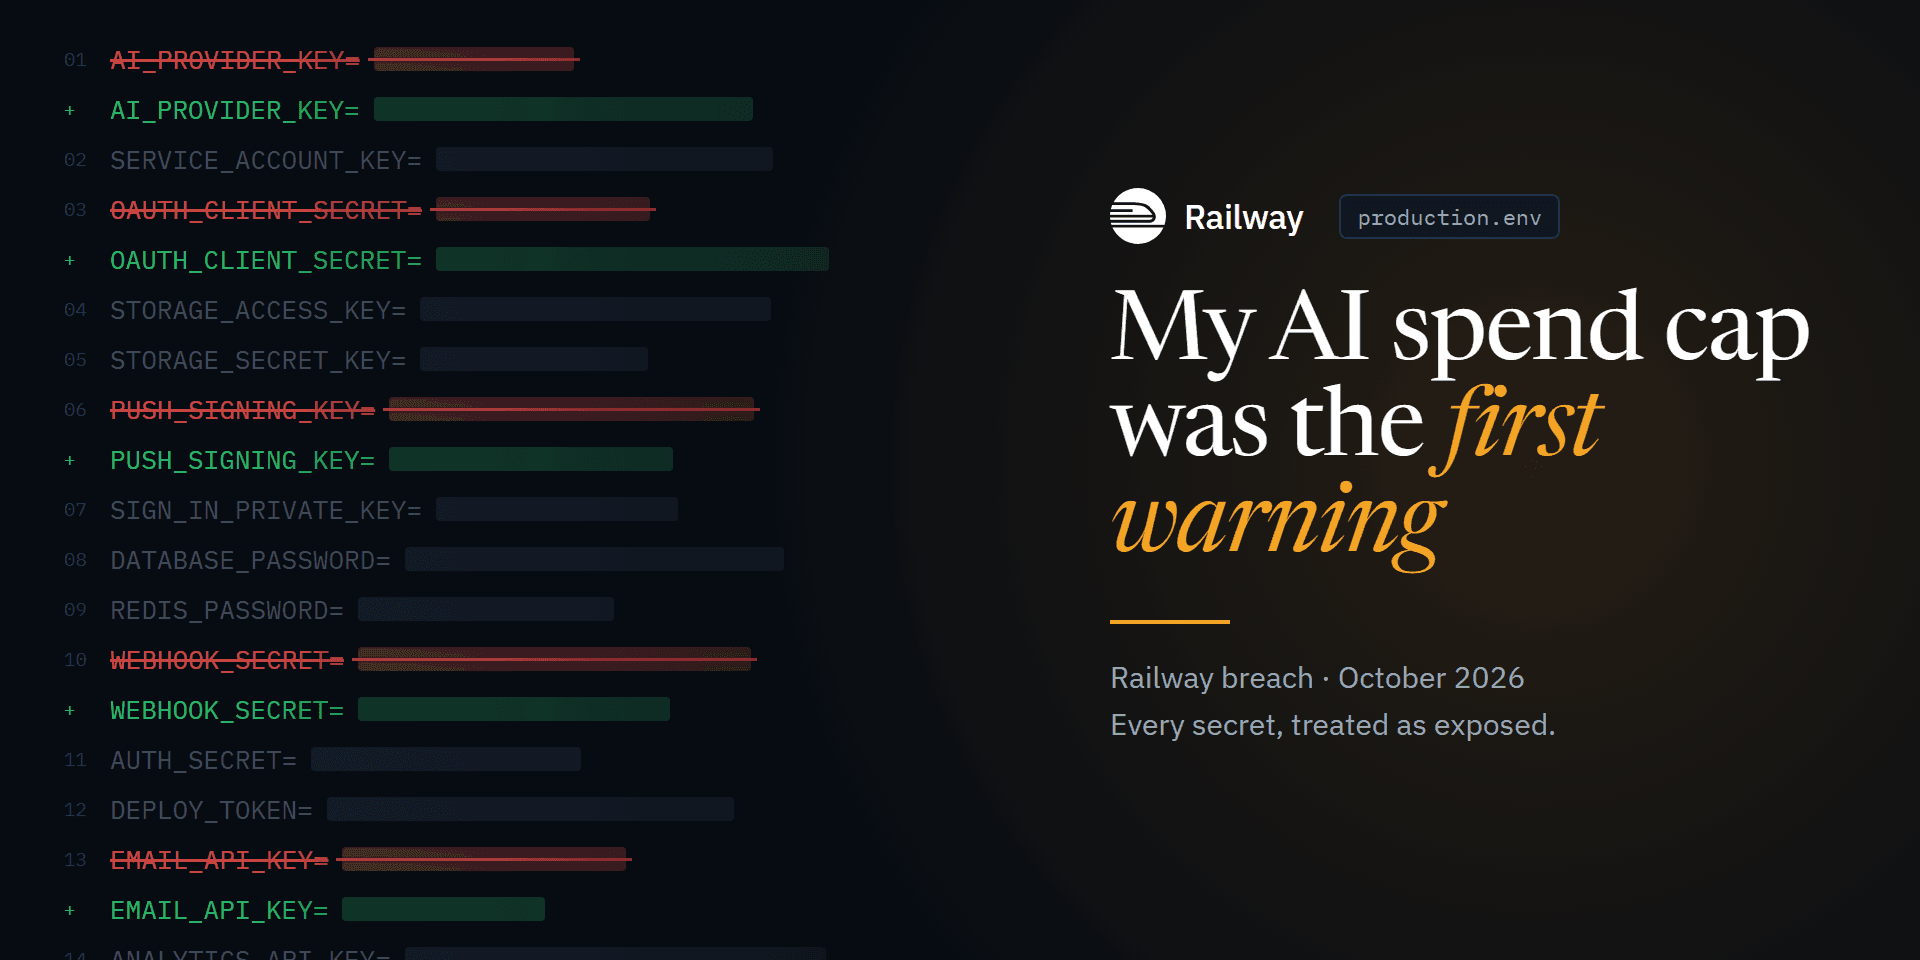
02 / Security Operations
A Gemini spend cap hit early was my first sign of the October 2026 Railway security incident. Here's what rotating every production secret involved.
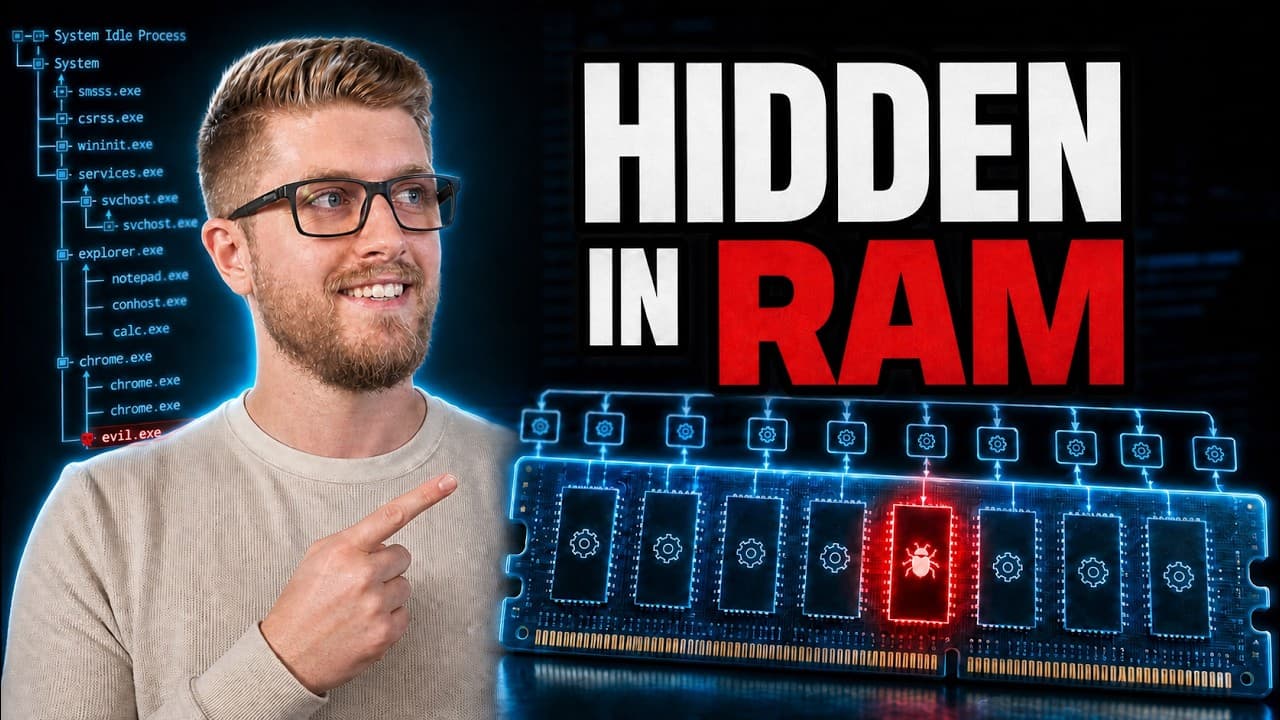
03 / Security Operations
Investigate Windows memory with Volatility 3: reconstruct process trees, inspect DLLs and handles, and assess suspicious code in two TryHackMe lab cases.
From the YouTube comments
A few comments from viewers who found the videos useful in the real world, from lab setup walkthroughs to practical security tooling and incident response walkthroughs.
This is the coarse location a website can infer from your connection, without asking for GPS permission.
Resolving approximate signal…
Observed location
Locating…
A VPN can mask your public IP and change the location websites infer. It improves privacy, but it does not make you anonymous.
Affiliate link · I may earn a commission at no extra cost to you
Exposure report
Runs in your browser and nothing is stored. The WebRTC check contacts Cloudflare's public STUN server, the same thing a video call does.
Location is approximate and may reflect your ISP or VPN exit server.
Have a question, collaboration or speaking opportunity? Send the details and I'll get back to you as soon as possible.
Message composer
Routing details
On the YouTube channel
Practical cloud security, ethical hacking, career development and security implementation explained through repeatable, hands-on walkthroughs.
Channel trailer · 0:27
Live channel telemetry
For brands & partners
Interested in a relevant YouTube partnership?


